Rafay and Fortanix Bring Attested Confidential AI to Kubernetes Pods
What Actually Changed
Confidential AI is moving closer to where developers actually deploy it. Rafay Systems and Fortanix announced on Thursday, as KubeCon + CloudNativeCon North America 2026 wrapped up, that they have extended their joint offering from virtual machines down to individual Kubernetes pods. The Rafay Platform now orchestrates workloads running on CNCF Confidential Containers (CoCo) with Fortanix Confidential AI, letting neoclouds, sovereign AI clouds and enterprises offer confidential AI as a managed service. Here's the thing: the partnership already worked at the virtual machine level, so this is less a new product than a change in the unit of deployment. Pods are what most teams think in when they ship containerized AI, and that's why the move matters more than the announcement's tone suggests.
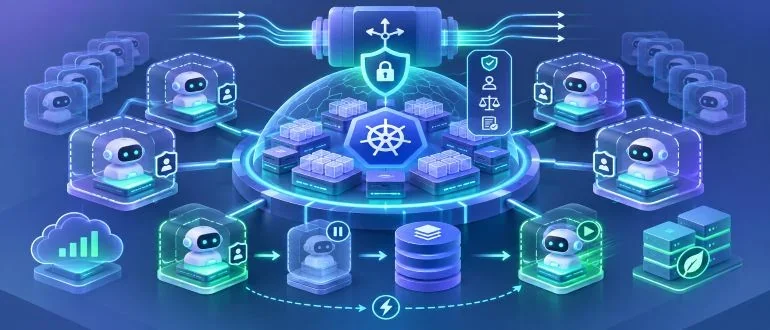
CoCo is a CNCF incubating project built on Kata Containers. Each pod runs in its own lightweight confidential virtual machine, with memory encrypted by the CPU. On supported hardware, GPUs fall inside the trust boundary too. That's the part to watch. AI inference is GPU-heavy, and a boundary that ignored the accelerator would leave the most sensitive computation exposed. (And this is the part most people overlook.) Plenty of confidential computing discussions stop at the CPU, even though a lot of sensitive data sits in GPU memory while a model runs. The hardware dependency deserves attention too. "Supported hardware" is doing real work in that sentence, and your options depend entirely on what your clusters run on.
The trust decision happens through attestation. Fortanix Confidential Computing Manager performs composite attestation across CPU and GPU trusted execution environments, plus firmware and software components. Fortanix Data Security Manager releases encryption keys only to environments that pass. If attestation fails, the keys stay locked and the workload can't reach sensitive data. That's a meaningful design choice. Instead of trusting that a container started in the right state, the system asks for proof and withholds secrets until the proof checks out. Attestation is still a measurement, though, and the outcome is only as good as what gets measured. Composite coverage across CPU, GPU, firmware and software is the detail to scrutinize when you evaluate this.
Packaging Confidential Workloads as a Service
Rafay handles the operations layer. Its blueprints install the Fortanix CoCo add-ons and keep them synchronized across every confidential cluster. Operators onboard GPU infrastructure once, then give each customer an isolated tenant. Administrators package a confidential workload as a SKU in Rafay SKU Studio, and end users launch it on demand from the Rafay Developer Hub without filing a support ticket. Policy, access controls and quotas apply across tenants and clusters. If you've ever run a GPU fleet for more than one customer, you know the pain rarely lies in the first installation. It lies in configuration drift months later, when one cluster has a slightly different add-on version than the rest. Blueprints that keep everything in sync are aimed squarely at that problem.
"With Confidential Containers, that model now reaches the Kubernetes pod, where AI teams already ship their workloads," said Mohan Atreya, chief product officer at Rafay. Anuj Jaiswal, chief product officer at Fortanix, said model owners, enterprises and operators each want assurance that the others can't see what they own. "Fortanix Confidential AI releases keys only to attested workloads," he said. Vendor launch quotes are positioning, so read them that way. Still, both executives frame the pitch around assurance for parties who don't control the underlying hardware. That's the right audience. The tenancy model is the more interesting claim, and I'd want to see it tested under real multi-customer load before I took it at face value.
Availability and the Verification Gap
The Rafay side of CoCo-based deployments with Fortanix Confidential AI is available now, running alongside the confidential VM integration the two companies already offered. Fortanix first announced its Confidential AI support for CoCo on Oct. 19, so Thursday's release is a second step in a sequence rather than a standalone debut. That means the Fortanix half has been public for a while, and the Rafay orchestration layer is the newer piece you'll need to evaluate on its own terms.
The timing points to a gap the companies say is real. Research from Fortanix and Atomik Research found that 93% of AI leaders understand traditional encryption doesn't protect data while AI processes it, yet only half can fully verify that protection is in place during inference. That's the buyer problem this stack targets. Attestation enforced at the pod level, rather than assumed, turns a vague security promise into something operators can actually check. Keep in mind that this is survey research co-produced by one of the vendors, so the 93% figure reflects what leaders say they understand, not a measured exposure rate. Still, the gap between knowing and verifying is a familiar pattern in security, where awareness runs well ahead of implementation.
What This Means for Teams Building on It
If you're running AI workloads with regulated or proprietary data, the practical question isn't whether this works. It's who inherits the operational burden. Packaging confidential compute as a SKU moves much of that burden away from individual application teams, which helps if your platform team has the capacity to support it. Similar confidential computing offerings typically bring hardware constraints, attestation policies that need ongoing maintenance and key management dependencies. Plan time for those, because they won't disappear just because the self-service portal looks clean.
Here's my read: moving the boundary down to the pod is the right direction, and it's more significant than the press release makes it sound. The part I'd hold back on is the assumption that attestation solves trust by itself. It proves a specific configuration was measured and matched expectations. It doesn't prove the model behaves well, that the data pipeline upstream is clean, or that the people operating the platform have made sound decisions. That said, a pipeline where keys stay locked until proof arrives is a better starting point than most AI deployments offer today.
What happens next depends on how quickly GPU-level confidential computing reaches hardware that neoclouds and enterprises already own. I won't guess at timelines, because nothing in the announcement gives me a basis for one. What I'd watch is whether customers start asking for attestation evidence as a formal requirement in their vendor agreements. That's where the "verify, don't assume" pitch either becomes operational reality or stays a slide. Promising. Unproven at production scale, for now.